Aepto Domain Expiry, SSL, DNS & PHP Security
Aepto Domain Expiry, SSL, DNS & PHP Security
Description
WordPress Site Health watches PHP, cron, and plugins. It does not watch whether your domain is about to expire, whether DNS still points at this install, or whether SPF/DKIM/DMARC will dump order email into spam.
Domain Anchor (free, no Aepto account) watches that layer for this site only — and when a critical PHP RCE hits (starting with CVE-2026-109618 / CVE-2026-109619 — php2shell), it emails your contacts and gives you a copy-ready hosting support ticket.
Free — works the moment you activate
- Domain registration expiry — days left + registrar when the registry publishes it
- SSL / TLS certificate expiry — days left + issuer
- DNS snapshot — A / AAAA / NS (and change journal when records move)
- Tether check — confirms the public hostname still serves this WordPress (not “A record equals server IP”, which breaks behind Cloudflare)
- Email authentication grade — SPF, DKIM, DMARC, MX from public DNS
- PHP security — checks this server’s PHP version against critical advisories (starting with php2shell); admin notice + copy-ready support ticket for your host; repeat emails until patched
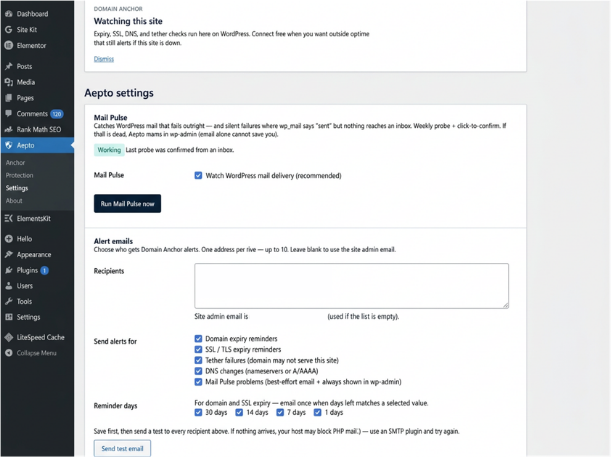
- Email alerts — choose up to 10 recipients; toggle domain / SSL / tether / DNS / Mail Pulse / PHP alerts; pick reminder days (30 / 14 / 7 / 1)
- Mail Pulse — weekly delivery probe with click-to-confirm; catches silent wp_mail failures; loud wp-admin warning when mail is dead
- Test email — Settings Send test email to all recipients (if it fails, use an SMTP plugin — many hosts block PHP mail())
- Admin bar chip — quick Domain / SSL countdown (or PHP: critical when an advisory hits)
- Dashboard widget — at-a-glance risks
- Continuity report (PDF) — dense client-ready PDF (expiry, tether, DNS, email auth, Mail Pulse, PHP security); Connected adds outside uptime %, stability, latency, downtime history
No account. No API key. No front-end scripts on your public site.
Optional — Connect free with Aepto
Sign in with Aepto (OAuth, no pasted secrets) to protect this WordPress from the outside:
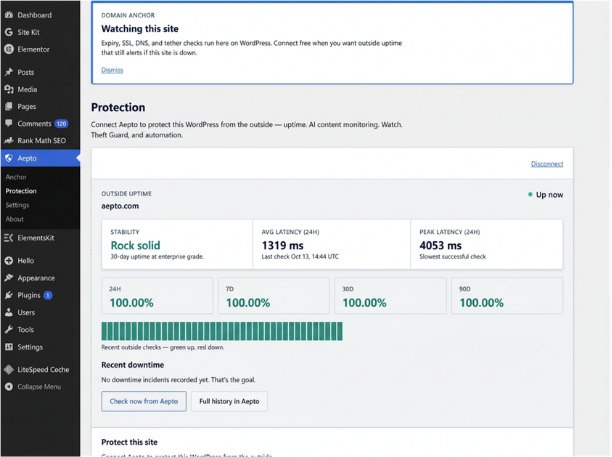
- Outside uptime board in Protection — live status, 24h/7d/30d/90d uptime %, stability, latency, downtime duration history (alerts even if WordPress cannot send mail)
- Add this site to your Aepto portfolio
- Domain Watch and Theft Guard
- Attention inbox in wp-admin
- Open the full Aepto dashboard for this domain
Paid Aepto plans (checkout on app.aepto.com)
- AI page monitoring — catch white screens, critical / database errors, and “uptime green but the page is broken”
- Alert webhooks — push incidents to Slack, tickets, Zapier, on-call tools
The free Domain Anchor stays fully usable forever. Connect and paid features are optional upgrades, not a crippled teaser.
Who this is for
- Site owners who renew domains once a year and forget
- WooCommerce / form sites that need mail to actually deliver
- Agencies who need a clean continuity report for clients
- Anyone who needs to push their host to patch critical PHP CVEs quickly
- Anyone who has been burned by DNS pointing somewhere else
External services
This plugin may contact third-party / external services as follows:
- Your site’s hostname — TLS certificate probe and tether self-check against the public hostname of this WordPress site. Data sent: HTTPS connection to your own host (no third-party account). Runs when you run Domain Anchor or on the scheduled cron.
- Public DNS resolvers (via PHP DNS functions / the server’s configured resolvers) — used to read A, AAAA, NS, MX, and TXT records for email authentication grading and DNS snapshots. Data sent: the domain name being queried. Runs during Domain Anchor checks.
- RDAP bootstrap (RDAP.org) — used to look up domain registration expiry / registrar data when available. Data sent: the domain name in an HTTPS RDAP query. Service info: https://about.rdap.org/ (includes privacy considerations). Terms / policy: https://about.rdap.org/
- Verisign RDAP — fallback / TLD RDAP lookup for supported zones (for example .com). Data sent: the domain name in an HTTPS RDAP query. Terms of use: https://www.verisign.com/legal-center/rdap-terms/ — Privacy: https://www.verisign.com/legal-center/privacy/
- Aepto (https://app.aepto.com) — only when you Connect, opt in to anonymous install stats, or load optional outside-uptime / Protection data. Data may include install id, site URL/host, OAuth tokens you authorize, and monitoring identifiers you enable. Privacy: https://aepto.com/privacy — Terms: https://aepto.com/terms
PHP security checks use the local PHP_VERSION only (no remote vulnerability API call).
No third-party ads or analytics scripts are injected on the public front end of your site.
Aepto is a product of Limitless Hosting. Learn more at aepto.com.
Installation
- Install and activate from Plugins, or upload the plugin folder.
- Open Aepto Anchor and click Run check now.
- Open Aepto Settings, set alert recipients, then Send test email (alerts use WordPress mail).
- See Aepto About for the full free / Connect / paid feature list.
- Optional: Protection Connect free with Aepto (site must be reachable over HTTPS for Connect).
Screenshots
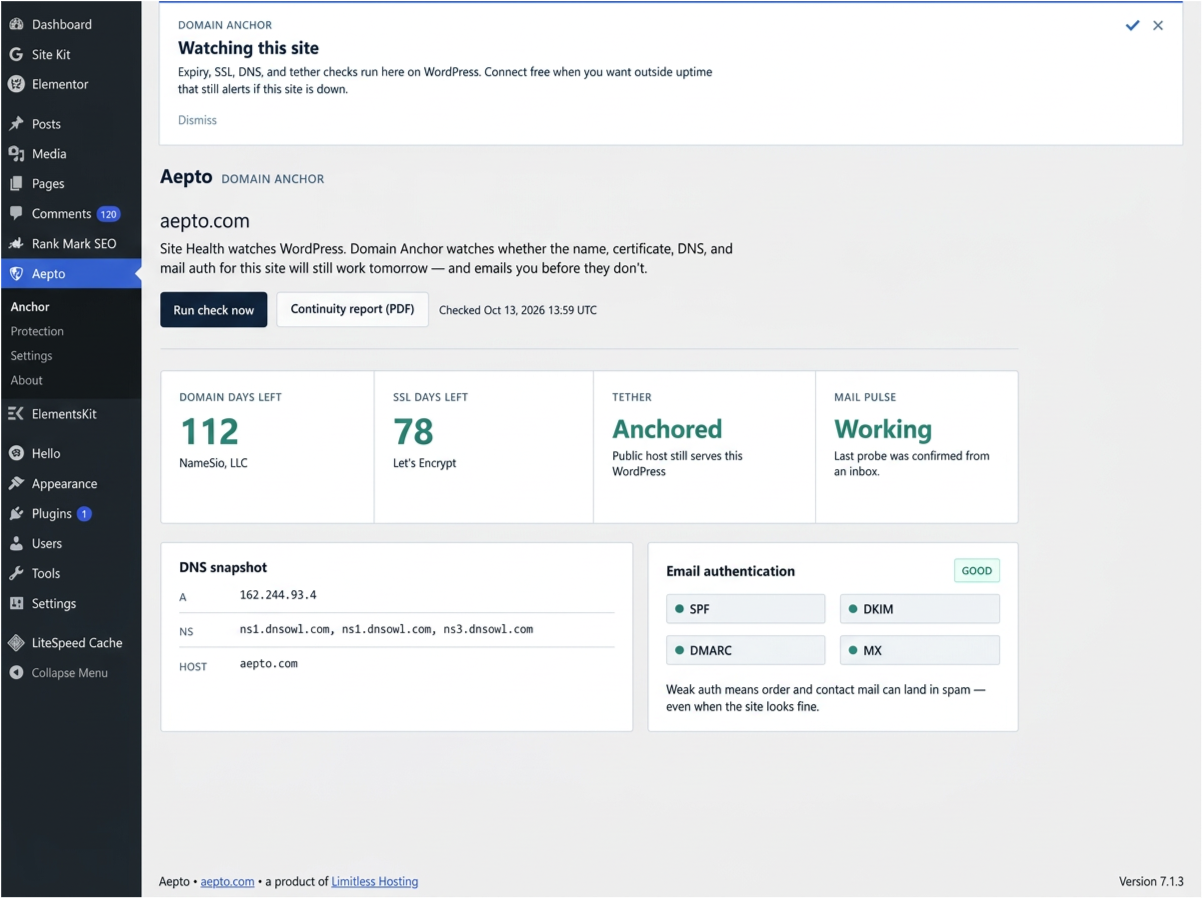
Domain Anchor — countdown, DNS, email auth
Admin bar status chip
Protection when connected
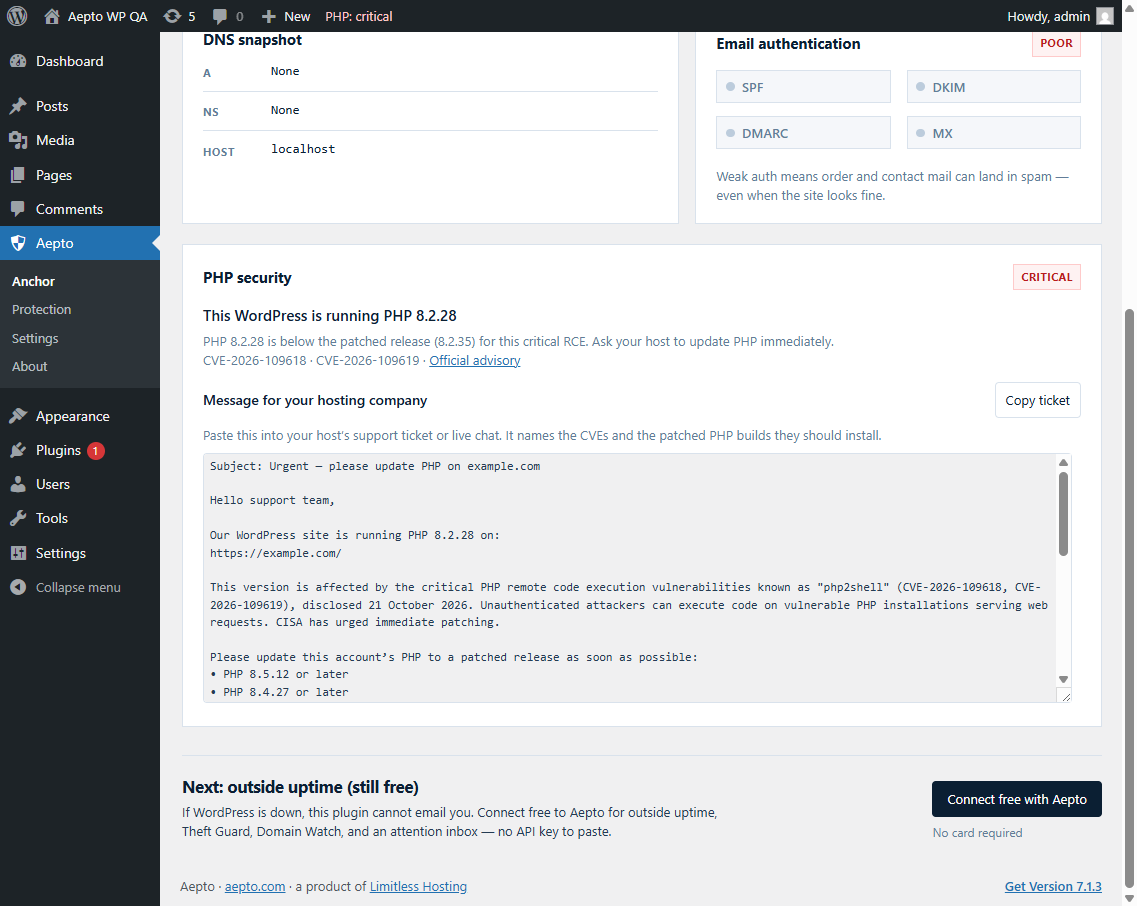
PHP security — critical advisory + host upgrade ticket
Faq
Yes. Domain Anchor — expiry, SSL, DNS, tether, email auth, PHP security, wp_mail alerts, admin bar, report — runs on your WordPress host with zero Aepto login.
Site Health checks the WordPress engine (PHP, cron, plugins) at a high level. Aepto Domain Anchor checks the domain layer: registration, certificate, DNS drift, tether, and mail authentication — and adds critical PHP CVE alerts with a crafted message you can paste to your hosting company.
Aepto ships a curated list of critical PHP runtime advisories (starting with php2shell: CVE-2026-109618 and CVE-2026-109619). It compares your server’s PHP version to the patched floors from the PHP project, and understands CloudLinux / cPanel ea-php (and alt-php) security backports — including older EOL branches where the host may have backported fixes but you should still plan an upgrade.
Checks run in wp-admin and via WP-Cron. There is no front-end HTML/JS/CSS by default. A small public REST route exists only for the tether challenge.
By default: domain and SSL countdown emails at 30, 14, 7, and 1 days, plus immediate mail on tether failure or significant DNS change — to the site admin email. Mail Pulse also sends a periodic probe with a confirm link; if WordPress claims “sent” but nobody confirms, Aepto flags a silent failure and warns in wp-admin (because broken mail cannot reliably email you). Critical PHP alerts repeat (day 0, 3, 7, then weekly) until the version is patched or you turn PHP alerts off. In Settings you can add recipients, toggle alert types, and Run Mail Pulse now.
Nothing until you Connect or opt in to anonymous install stats. After Connect, only what you authorize (domains, monitoring, etc.). PHP security evaluation stays on your WordPress host.
Yes for Domain Anchor UI and tether. Public RDAP / SSL / DNS for localhost will often show empty — use a real domain for full data. Connect free with Aepto requires a public HTTPS site (Aepto rejects http:// callbacks, including local Docker). That “Invalid Redirect” message on Connect from localhost is expected, not a broken upgrade link.
Reviews
Excellent free WordPress monitoring plugin
By 
Really useful plugin! My website emails used to stop working without me even knowing, so the email monitoring is a huge help. Now I can keep an eye on everything and get alerts if something goes wrong. It also monitors domain expiry, SSL and DNS. The best part? It’s all completely free! Highly recommend it for any WordPress site owner.
Reliable Monitoring
By 
Aepto Domain Expiry, SSL & DNS Monitor is a useful tool for keeping track of domain renewals, SSL certificates, and DNS health in one place. I like how it helps simplify domain management and makes it easier to stay ahead of potential issues before they affect a website. The centralized monitoring and timely alerts are especially helpful for anyone managing multiple domains. I have integrated with my multiple sites and recommend it to all of my clients.
Changelog
1.1.1
- PHP security: CloudLinux / ea-php (alt-php) backport awareness for php2shell (CVE-2026-109618 / CVE-2026-109619) — reduces false positives when the host already applied a vendor backport but PHP_VERSION stays below php.net
- EOL branches with a recognized backport show as “backported with upgrade recommended” instead of an unpatched critical
- Host ticket includes package confirm steps when a CloudLinux stack is detected
1.1.0
- PHP security: critical advisory checks (php2shell / CVE-2026-109618 & CVE-2026-109619), admin notice, repeat email alerts, and a copy-ready hosting support ticket
- Display name / tags / description updated for PHP security discoverability (slug unchanged)
1.0.1
- Review fixes: Aepto-first display name, documented RDAP services, PDF library prefix, Mail Pulse confirm page, scoped notices, remove unnecessary textdomain load
1.0.0
- Initial release: Domain Anchor, Connect, Protection, settings, continuity report